A sophisticated North Korean cyber group is weaponizing the crypto industry's own talent hunger, turning job interviews into malware delivery mechanisms.
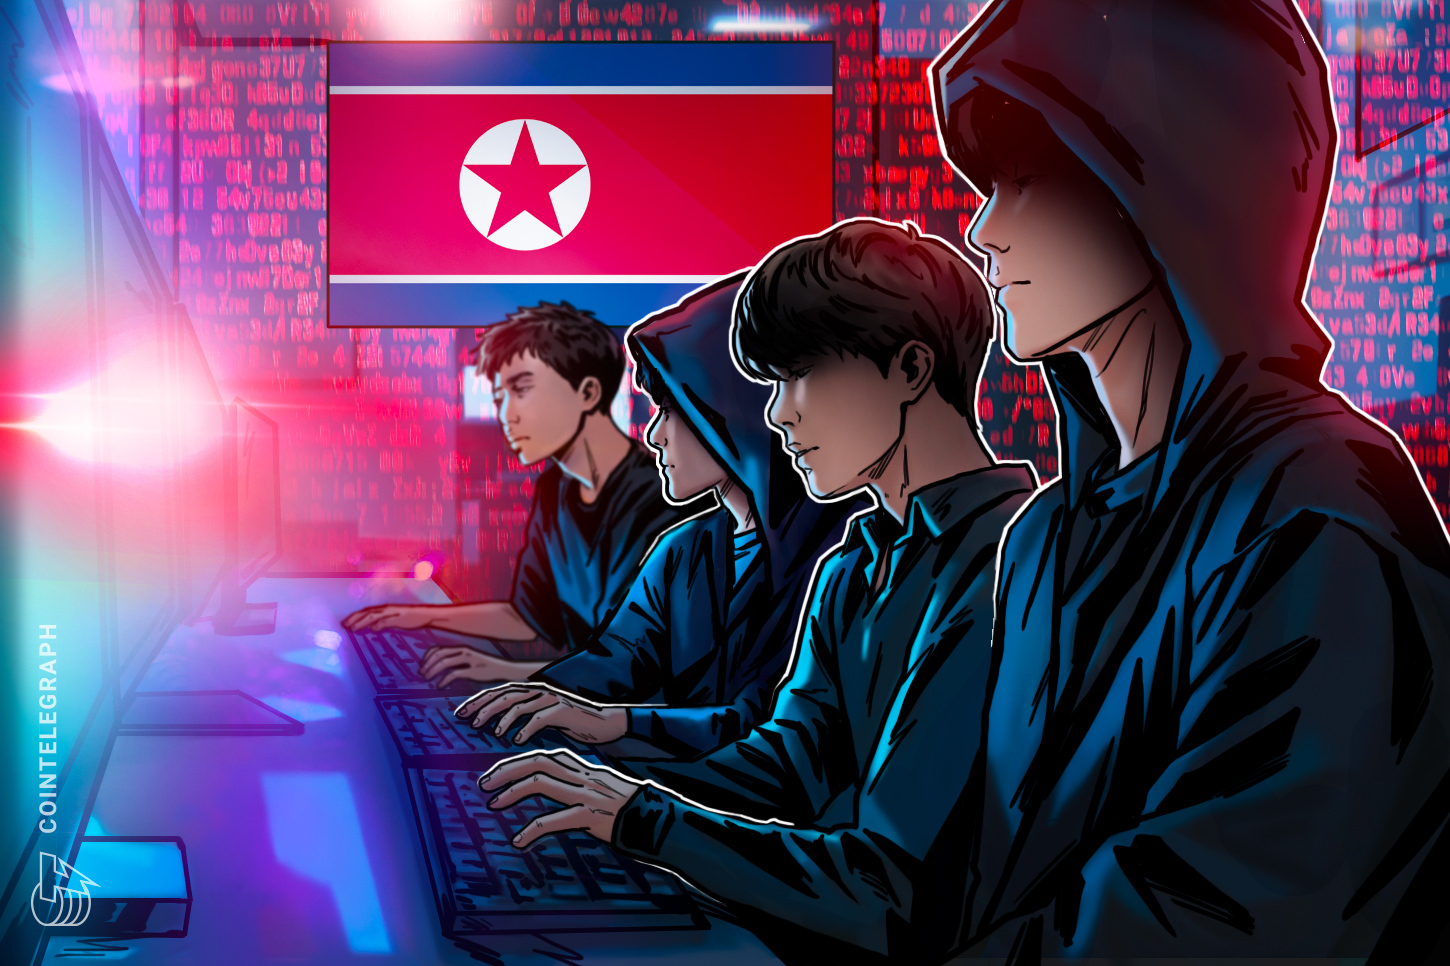
North Korean Hackers Pose as Recruiters, Infect 30K Devices and Steal $10.7M in Crypto
The WaterPlum cyber group has been running what amounts to a catfish operation at scale, impersonating recruiters for crypto, AI, and NFT companies to lure developers into downloading malicious software. According to Cointelegraph, the campaign has infected roughly 30,000 devices and extracted $10.7 million in cryptocurrency—a haul that underscores both the sophistication of nation-state actors and the peculiar vulnerabilities of a sector built partly on the premise that pseudonymity keeps you safe.
What makes this campaign noteworthy isn't just the theft amount, though that's significant. It's the targeting methodology. Job interviews represent a moment when targets are relaxed, hopeful, and credulous—they're being offered something they want, which is exactly when people drop their guard. For developers active in crypto, the offer of a position at a prominent blockchain company probably felt like genuine opportunity, not a pretext for infection. The attack surface here is social engineering layered over technical delivery, and it works.
The incident is a reminder that crypto's security theater—hardware wallets, multisig, self-custody—doesn't matter if the device holding your keys gets compromised before you even know you're a target. North Korea, apparently, is quite interested in the sector's liquidity, and they're patient enough to build elaborate false identities to access it.
Read more at Cointelegraph →